India's No.1 PU & Degree With Integrated IAS & IPS(UPSC/PSC) Training College.

PHP Security Flaws Expose Websites to Attacks
PHP SECURITY FLAWS EXPOSE WEBSITES TO REMOTE ATTACKS
WHY IN THE NEWS
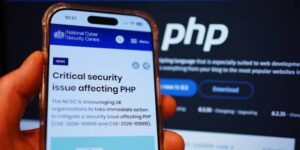
- Security Disclosure: On October 21, 2026, the PHP development team disclosed two serious security vulnerabilities that could enable attackers to execute malicious code remotely.
- Urgent Action: Security fixes are available, requiring website owners and organisations to update affected PHP systems and investigate potential security breaches to protect sensitive information.
Understanding PHP Vulnerabilities and Associated Risks:
- PHP Explained: PHP (PHP: Hypertext Preprocessor) is a server-side programming language widely used to develop dynamic websites, online shopping platforms, news portals, blogs, and business applications.
- Memory Corruption: The first vulnerability involves improper handling of memory when PHP encounters memory shortages and cleans up partially processed data.
- Stale References: The second flaw involves a reference to memory that has already been released, potentially causing the program to access invalid or unexpected data.
- Remote Code Execution: Attackers could exploit these weaknesses to execute malicious code remotely on vulnerable servers without requiring physical access or conventional authentication.
- Data Security Threats: Successful exploitation may expose personal information, passwords, and confidential records, enable website modification, and potentially allow attackers to compromise server operations.
Impact, Disclosure and Cybersecurity Measures
- Underlying Weakness: Since the vulnerabilities exist within PHP itself, attackers may exploit them before website-level security mechanisms, such as login checks, can provide protection.
- Discovery Timeline: According to the article, the first flaw was identified during a security review in 2024. Both vulnerabilities were publicly disclosed in October 2026, alongside fixes.
- Patching Priority: Website administrators must install the relevant security updates and inspect every affected environment, including production servers, testing systems, and internal applications.
- Breach Investigation: Organisations should examine server logs and systems for suspicious activity. If compromise is suspected, they may need to reset credentials, remove malicious changes, and rebuild affected systems.
- Shared Responsibility: Managed-hosting customers should confirm that their providers have installed the patches, while individual users generally depend on website operators to secure their systems.
ABOUT PHP AND CYBERSECURITY:● Server-Side Scripting: PHP processes requests on web servers and generates dynamic content delivered to users’ browsers. ● Remote Code Execution (RCE): RCE is a cybersecurity vulnerability that allows an attacker to run unauthorised commands or code on a remote system. ● Memory Corruption: This occurs when software incorrectly accesses or modifies memory, potentially causing crashes, unexpected behaviour, or security breaches. ● Cybersecurity Principles: Effective protection requires timely patching, access controls, continuous monitoring, secure software development, and incident response planning. |